Quick answer: Accountability for AI-assisted work always sits with people: the team member who reviews and approves the output, and ultimately the business that publishes or acts on it. Well-run AI-augmented teams make this explicit with named reviewers, documented sign-off steps and audit trails showing what was AI-drafted and human-approved.
Every business adopting AI eventually meets this question, usually at the worst possible moment. For example, a wrong figure reaches a client. A drafted reply promises something it should not have. Then, someone says “the AI did it”. This guide ensures that excuse never ends the conversation in your business, because it never works as one.
Can I blame the AI tool if something goes wrong?
No, and not merely as a matter of ethics. Legally, commercially and reputationally, the output belongs to the business that shipped it.
Your customer’s contract is with you, not with a model vendor. The regulator’s question is what controls your business had, not what the software intended; Australian government guidance on AI adoption is built on exactly this principle of human accountability for AI-assisted outcomes. And your client’s trust attaches to the name on the work. The tool is a how; responsibility follows the who, and the who is always a person in your chain.
This is less frightening than it sounds, because has always worked this way. A partner is accountable for a junior’s draft; a business is accountable for a supplier’s component. AI slots into an accountability structure every business already runs. The failure mode is not AI; it is shipping work no named person ever owned.
How do I structure sign-off for AI-assisted work?
Give every output one named owner, match the depth of review to the stakes, and keep a trail. A sign-off structure that fits on a page:
| Output type | Review required | Who signs off | Trail kept |
|---|---|---|---|
| Client-facing, financial or compliance outputs | Full review against source, every item | Named team member; manager countersign for commitments | Draft, corrections, approver, timestamp |
| High-volume structured work (reconciliation, categorisation) | Exception review: AI flags, human decides | The workflow’s named operator | Exception log with decisions |
| Mature internal workflows with a clean track record | Scheduled spot-checks and audits | The named operator; manager audits monthly | Sample results and error rates |
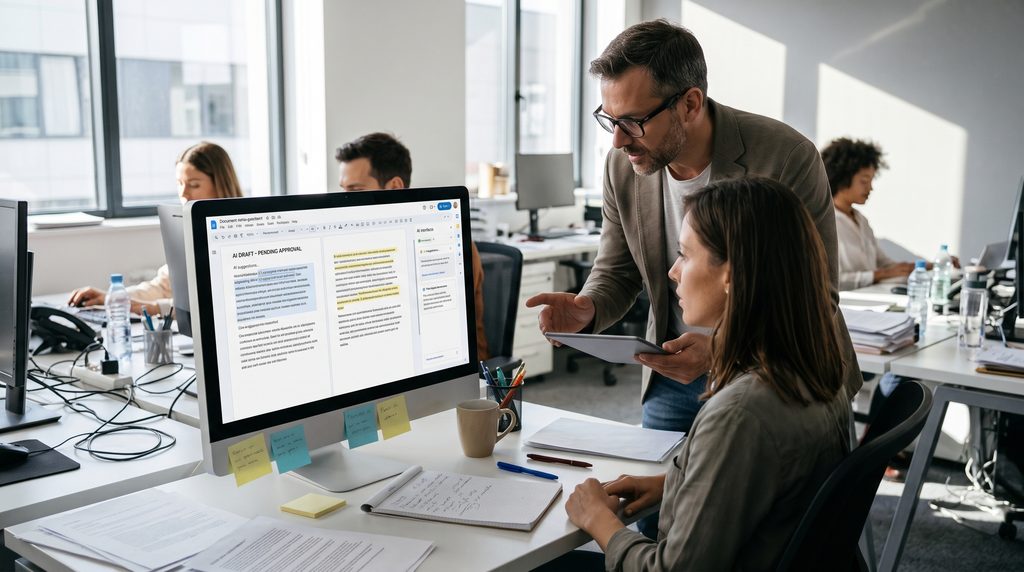
Three rules keep the table honest. New workflows always start in the top row and earn their way down as error rates prove out. The owner is a name, never a team. And ‘AI-drafted, human-approved’ is recorded, not remembered: when a question comes months later, the trail answers it in minutes.
What does responsible AI use look like in an SME?
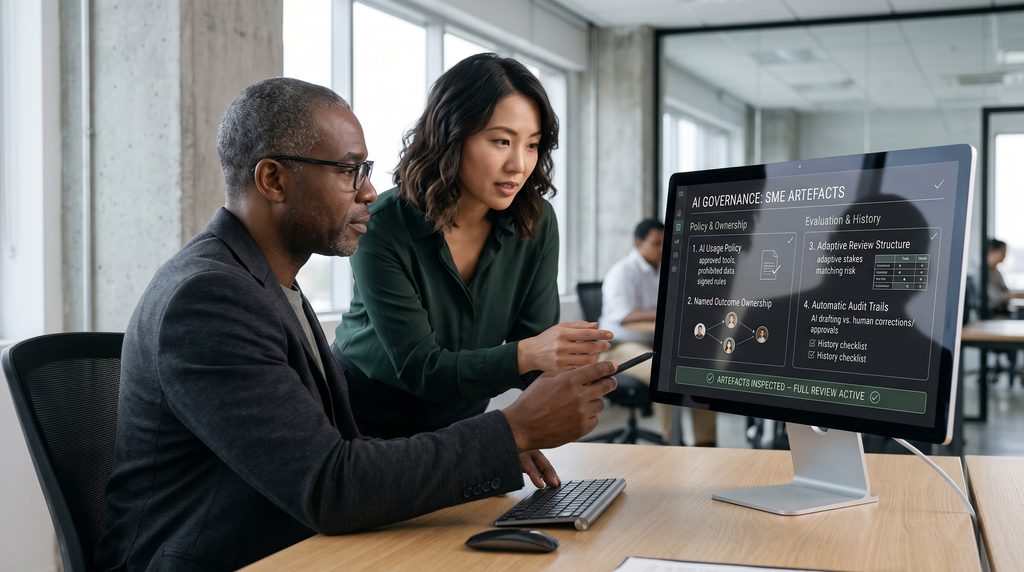
Four artefacts, all small, all inspectable:
- An AI usage policy naming approved tools, prohibited data and the sign-off rules, signed by everyone who uses the tools
- Named ownership of every workflow’s output, visible in the workflow documentation itself
- A review structure matched to stakes, like the table above, rather than a blanket rule that is either suffocating or ignored
- Audit trails showing what was AI-drafted, what was corrected and who approved, kept automatically where the work happens
Responsible use is not a committee or a 40-page framework; at SME scale it is these four artefacts plus the habit of starting every new workflow at full review. The businesses that struggle are rarely the ones with small governance; they are the ones with none, discovering it after the first incident.
What this means for your AI rollout
Accountability is a design input, not a post-incident patch. Decide the owner, the review tier and the trail when the workflow is built and the blame question answers itself before it is ever asked.
Every Hyvid workflow ships with this structure as standard: a named team member accountable for each output, review tiers agreed with you up front, and trails your auditors can read. If governance is the conversation your board or your clients are starting, talk to us about governance.
Frequently asked questions
A named person, always: the team member who reviewed and approved the output, inside a business that remains accountable for what it publishes or acts on. The tool is never the answer to ‘who’.
No. Contracts, regulators and clients all attach responsibility to your business, and Australian government guidance treats human accountability for AI-assisted outcomes as the operating principle. Structure for it rather than arguing with it.
One named owner per output, review depth matched to stakes (full review, exception review or audited spot-checks), a manager countersign on commitments, and an automatic trail of what was drafted, corrected and approved.
Every output needs a human owner; the depth of review varies by stakes and track record. Client-facing and financial work gets full review, high-volume structured work runs on exception review, and only mature, measured workflows graduate to spot-checks.
The draft, the corrections, the approver and the timestamp, kept automatically where the work happens. The test is whether, six months later, you could answer ‘who approved this and what did they change’ in minutes.